Programming

Microsoft is Creating a New Rust-Based Programming Language For Secure Coding (zdnet.com) 69

Under Project Verona, Microsoft is working to make Windows 10 more secure by integrating Mozilla-developed Rust for low-level Windows components. "'Memory safety' is the term for coding frameworks that help protect memory space from being abused by malware," reports ZDNet. "Project Verona at Microsoft is meant to progress the company's work here to close off this attack vector." From the report: Microsoft's Project Verona could turn out to be just an experiment that leads nowhere, but the company has progressed far enough to have detailed some of its ideas through the UK-based non-profit Knowledge Transfer Network. Matthew Parkinson, a Microsoft researcher from the Cambridge Computer Lab in the UK who's dedicated to "investigating memory management for managed programming languages," gave a talk last week focusing on what the company is doing to address these memory issues.

In the talk, Parkinson discussed the work Microsoft has done with MemGC, which is short for Memory Garbage Collector, for Internet Explorer (IE) and Edge. MemGC addressed vulnerabilities in the standard browser feature known as a Document Object Model (DOM), a representation of the data used by browsers to interpret web pages. Google's elite Project Zero hackers were impressed with Microsoft's MemGC after canvassing major browsers. [...] The other class of bugs Microsoft is working on to address relates to uninitialized memory in a way that also doesn't kill performance. [...] Parkinson said Microsoft is rewriting some "targeted" components in Rust. His talk focused on language design and compartmentalization. "If we want compartments, and to carve up the legacy bits of our code so [attackers'] exploit code can't get out, what do we need in the language design that can help with that?" This is Project Verona and Parkinson said it was the first time he'd discussed the project, which will be made open source "soon". It is a new language for what Microsoft is calling "safe infrastructure programming."
"The challenge for Microsoft is dealing with the 'application spectrum,' which spans from C# for desktop apps through to C and C# for Exchange, ASP.NET, Azure, and device drivers, to deep Windows components like memory management and boot loaders and the Windows kernel hardware abstraction layer (HAL)," the report says.

"The ownership model in Verona is based on groups of objects, not like in Rust where it's based on a single object," said Parkinson. "In C++ you get pointers and it's based on objects and it's pretty much per object. But that isn't how I think about data and grammar. I think about a data structure as a collection of objects. And that collection of objects as a lifetime. So by taking ownership at the level of ownership of objects, then we get much closer to the level of abstraction that people are using and it gives us the ability to build data structures without going outside of safety."
Security

Vulnerability In Fully Patched Android Phones Under Active Attack By Bank Thieves (arstechnica.com) 98

An anonymous reader quotes a report from Ars Technica: A vulnerability in millions of fully patched Android phones is being actively exploited by malware that's designed to drain the bank accounts of infected users, researchers said on Monday. The vulnerability allows malicious apps to masquerade as legitimate apps that targets have already installed and come to trust, researchers from security firm Promon reported in a post. Running under the guise of trusted apps already installed, the malicious apps can then request permissions to carry out sensitive tasks, such as recording audio or video, taking photos, reading text messages or phishing login credentials. Targets who click yes to the request are then compromised.

Researchers with Lookout, a mobile security provider and a Promon partner, reported last week that they found 36 apps exploiting the spoofing vulnerability. The malicious apps included variants of the BankBot banking trojan. BankBot has been active since 2017, and apps from the malware family have been caught repeatedly infiltrating the Google Play Market. The vulnerability is most serious in versions 6 through 10, which account for about 80% of Android phones worldwide. Attacks against those versions allow malicious apps to ask for permissions while posing as legitimate apps. There's no limit to the permissions these malicious apps can seek. Access to text messages, photos, the microphone, camera, and GPS are some of the permissions that are possible. A user's only defense is to click "no" to the requests.
"The vulnerability is found in a function known as TaskAffinity, a multitasking feature that allows apps to assume the identity of other apps or tasks running in the multitasking environment," reports Ars Technica. While Google has removed the [unnamed] malicious apps from its Play Store, according to Promon, the vulnerability is still unfixed in all versions of Android.

"Promon is calling the vulnerability 'StrandHogg,' an old Norse term for the Viking tactic of raiding coastal areas to plunder and hold people for ransom," the report adds. "Promon researchers said they identified StrandHogg after learning from an unnamed Eastern European security company for financial institutions that several banks in the Czech Republic reported money disappearing from customer accounts."
Software

Putin Signs Law Making Russian Apps Mandatory On Smartphones, Computers (reuters.com) 64

Russian President Vladimir Putin on Monday signed legislation requiring all smartphones, computers and smart TV sets sold in the country to come pre-installed with Russian software. Reuters reports: The law, which will come into force on July 1 next year, has been met with resistance by some electronics retailers, who say the legislation was adopted without consulting them. The law has been presented as a way to help Russian IT firms compete with foreign companies and spare consumers from having to download software upon purchasing a new device. The country's mobile phone market is dominated by foreign companies including Apple, Samsung and Huawei. The legislation signed by Putin said the government would come up with a list of Russian applications that would need to be installed on the different devices.
China

All New Cellphone Users In China Must Now Have Their Face Scanned (technologyreview.com) 69

An anonymous reader quotes a report from MIT Technology Review: Customers in China who buy SIM cards or register new mobile-phone services must have their faces scanned under a new law that came into effect yesterday. China's government says the new rule, which was passed into law back in September, will "protect the legitimate rights and interest of citizens in cyberspace." It can be seen as part of an ongoing push by China's government to make sure that people use services on the internet under their real names, thus helping to reduce fraud and boost cybersecurity. On the other hand, it also looks like part of a drive to make sure every member of the population can be surveilled. The Financial Times reported yesterday that tech companies in China are helping to create influential United Nations standards for the facial recognition technology, which will help shape rules on how facial recognition is used around the world.
IOS

iOS Apps Could Really Benefit From the Newly Proposed Security.plist Standard (zdnet.com) 13

Security researcher Ivan Rodriguez has proposed a new security standard for iOS apps, which he named Security.plist. From a report: The idea is simple. App makers would create a property list file (plist) named security.plist that they would embed inside the root of their iOS apps. The file would contain all the basic contact details for reporting a security flaw to the app's creator. Security researchers analyzing an app would have an easy way to get in contact with the app's creators. Rodriguez said the idea for Security.plist came from Security.txt, a similar standard for websites, that was proposed in late 2017. Security.txt is currently going through an official standardization process at the Internet Engineering Task Force (IETF), but it has been widely adopted already, and companies like Google, GitHub, LinkedIn, and Facebook, all have a security.txt file hosted on their sites, so bug hunters can get in touch with their respective security teams. Rodriguez, who is an amateur bug hunter in iOS apps, said he decided to propose a similar thing for iOS apps because getting in touch with an app's dev or security team has been a problem in the past. "I spend most of my free time poking mobile applications which has lead me to find many vulnerabilities and I have yet to find one that has an easy way to find the correct channel to responsibly disclose these issues,"Rodriguez told ZDNet.
Security

Now Even the FBI is Warning About Your Smart TV's Security (techcrunch.com) 126

If you just bought a smart TV on Black Friday or plan to buy one for Cyber Monday tomorrow, the FBI wants you to know a few things. From a report: Smart TVs are like regular television sets but with an internet connection. With the advent and growth of Netflix, Hulu and other streaming services, most saw internet-connected televisions as a cord-cutter's dream. But like anything that connects to the internet, it opens up smart TVs to security vulnerabilities and hackers. Not only that, many smart TVs come with a camera and a microphone. But as is the case with most other internet-connected devices, manufacturers often don't put security as a priority. That's the key takeaway from the FBI's Portland field office, which just ahead of some of the biggest shopping days of the year posted a warning on its website about the risks that smart TVs pose. "Beyond the risk that your TV manufacturer and app developers may be listening and watching you, that television can also be a gateway for hackers to come into your home. A bad cyber actor may not be able to access your locked-down computer directly, but it is possible that your unsecured TV can give him or her an easy way in the backdoor through your router," wrote the FBI. The FBI warned that hackers can take control of your unsecured smart TV and in worst cases, take control of the camera and microphone to watch and listen in.
Security

Millions of SMS Text Messages Exposed In Unencrypted Database (techcrunch.com) 17

"A massive database storing tens of millions of SMS text messages, most of which were sent by businesses to potential customers, has been found online," reports TechCrunch. The database belongs to a company that works with over 990 cell phone operators and reaches more than 5 billion subscribers around the world, according to the researchers.

TechCrunch writes: The database is run by TrueDialog, a business SMS provider for businesses and higher education providers, which lets companies, colleges, and universities send bulk text messages to their customers and students. The Austin, Texas-based company says one of the advantages to its service is that recipients can also text back, allowing them to have two-way conversations with brands or businesses.

The database stored years of sent and received text messages from its customers and processed by TrueDialog. But because the database was left unprotected on the internet without a password, none of the data was encrypted and anyone could look inside. Security researchers Noam Rotem and Ran Locar found the exposed database earlier this month as part of their internet scanning efforts... Many of the messages we reviewed contained codes to access online medical services to obtain, and password reset and login codes for sites including Facebook and Google accounts...

One table alone had tens of millions of messages, many of which were message recipients trying to opt-out of receiving text messages.

IT

Ask Slashdot: Is Your Company Using Linux Desktops? 198

SomeoneFromBelgium writes: Yesterday I spoke to a friend of mine who works for a company developing mostly integrated network solutions which are purely Linux-based. He complained that he was unable to convince his IT department to provide him and his fellow developers and testers with a Linux desktop. They stated that "it was more secure when using a VM".

We both agreed that the more likely problem is that the IT department is solely geared towards a Windows desktop environment and that they have neither the skills nor the inclination to support any other platform.

This got me wondering: is this also your experience?

I bet Slashdot's readers have stories to tell, with enlightening experiences in corporate workplaces over the years gone by. So feel free to share your thoughts, opinions, and anecdotes in the comments.

And is your company using Linux desktops?
Communications

SMS Replacement is Exposing Users To Text, Call Interception Thanks To Sloppy Telecos (vice.com) 32

A standard used by phone carriers around the world can leave users open to all sorts of attacks, like text message and call interception, spoofed phone numbers, and leaking their coarse location, new research reveals. From a report: The Rich Communication Services (RCS) standard is essentially the replacement for SMS. The news shows how even as carriers move onto more modern protocols for communication, phone network security continues to be an exposed area with multiple avenues for attack in some implementations of RCS. "I'm surprised that large companies, like Vodafone, introduce a technology that exposes literally hundreds of millions of people, without asking them, without telling them," Karsten Nohl from cybersecurity firm Security Research Labs (SRLabs) told Motherboard in a phone call.

SRLabs researchers Luca Melette and Sina Yazdanmehr will present their RCS findings at the upcoming Black Hat Europe conference in December, and discussed some of their work at security conference DeepSec on Friday. RCS is a relatively new standard for carrier messaging and includes more features than SMS, such as photos, group chats, and file transfers. Back in 2015, Google announced it would be adopting RCS to move users away from SMS, and that it had acquired a company called Jibe Mobile to help with the transition. RCS essentially runs as an app on your phone that logs into a service with a username and password, Nohl explained.

Security

Hacker Stole Unreleased Music and Then Tried To Frame Someone Else (zdnet.com) 41

US authorities charged a Texas man this week for hacking into the cloud accounts of two music companies and the social media account of a high-profile music producer, from where he stole unreleased songs that he later published online for free on public internet forums. From a report: When the man realized he could be caught, he contacted one of the hacked companies and tried to pin the blame on another individual. According to court documents published on Monday by the Department of Justice, the suspect is a 27-year-old named Christian Erazo, from Austin, Texas. US authorities say that Erazo worked with three other co-conspirators on a series of hacks that took place between late 2016 and April 2017. The group's primary targets were two music management companies, one located in New York, and the second in Los Angeles. According to investigators, the four hackers obtained and used employee credentials to access the companies' cloud storage accounts, from where they downloaded more than 100 unreleased songs. Most of the data came from the New York-based music label, from where the Erazo and co-conspirators stole more than 50 GBs of music. Erazo's indictment claims the group accessed the company's cloud storage account more than 2,300 times across several months.
Security

Only a Few 2020 US Presidential Candidates Are Using a Basic Email Security Feature (techcrunch.com) 88

Just one-third of the 2020 U.S. presidential candidates are using an email security feature that could prevent a similar attack that hobbled the Democrats during the 2016 election. From a report: Out of the 21 presidential candidates in the race, according to Reuters, only seven Democrats are using and enforcing DMARC, an email security protocol that verifies the authenticity of a sender's email and rejects spoofed emails, which hackers often use to try to trick victims into opening malicious links from seemingly known individuals. It's a marked increase from April, where only Elizabeth Warren's campaign had employed the technology. Now, the Democratic campaigns of Joe Biden, Kamala Harris, Michael Bloomberg, Amy Klobuchar, Cory Booker, Tulsi Gabbard and Steve Bullock have all improved their email security. The remaining candidates, including presidential incumbent Donald Trump, are not rejecting spoofed emails. Another seven candidates are not using DMARC at all.
Security

Hidden Cam Above Bluetooth Pump Skimmer (krebsonsecurity.com) 113

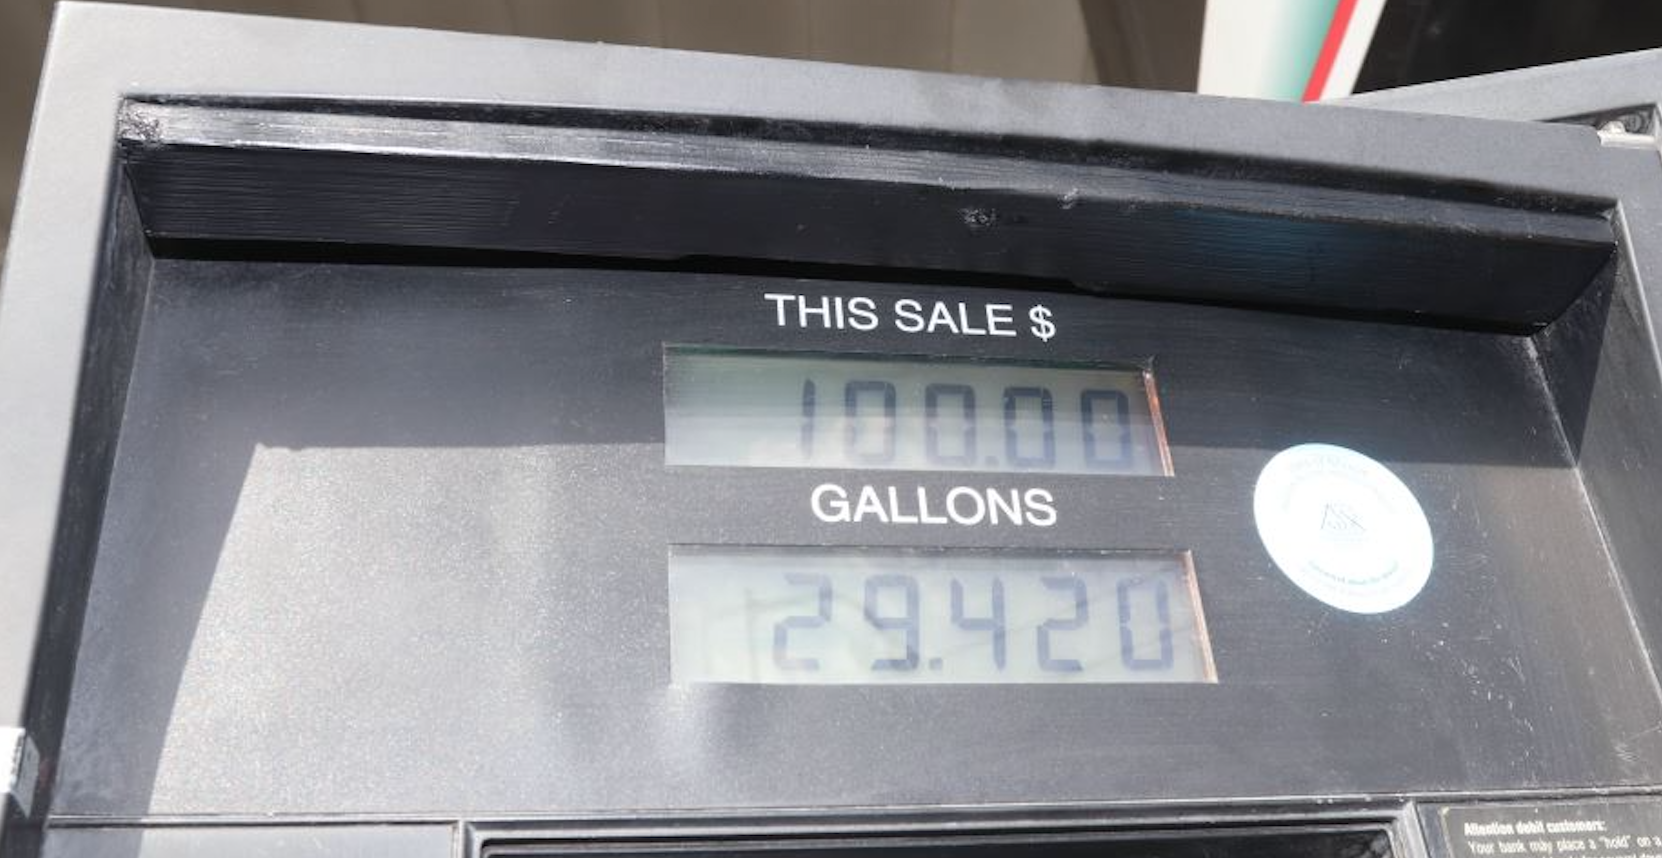
Brian Krebs: Tiny hidden spy cameras are a common sight at ATMs that have been tampered with by crooks who specialize in retrofitting the machines with card skimmers. But until this past week I'd never heard of hidden cameras being used at gas pumps in tandem with Bluetooth-based card skimming devices. Apparently, I'm not alone. "I believe this is the first time I've seen a camera on a gas pump with a Bluetooth card skimmer," said Detective Matt Jogodka of the Las Vegas Police Department, referring to the compromised fuel pump pictured here.

Image.

It may be difficult to tell, but the horizontal bar across the top of the machine (just above the 'This Sale $' indicator) contains a hidden pinhole camera angled so as to record debit card users entering their PIN.

IT

A Firmware Update Removed the Noise-Cancelling Function From Bose's Noise-Cancelling Headphones. No Word From Bose if It Plans To Fix It (theregister.co.uk) 138

Owners of Bose QuietComfort 35 headphones are still trying to get the company to either fix or roll back a firmware update that removed noise-cancelling functions from their over-ear gear. From a report: The problems date back to July and some owners seem to have managed to get Bose to exchange their cans for the company's shiny new 700 headphones. We were contacted by a reader who was first given a set of version II headphones when his V1 set were borked. When the updated firmware borked them as well, he declined the offer of a replacement set and was given a pair of 700s. Firmware version 4.5.2 was fingered as the main culprit. Like all Bose gear, the cans don't come cheap -- they'll set you back $335 to be precise, or $450 for a pair of limited edition white 700s. Pissed-off punters have filled a deafening 182 pages of Bose's support forums with complaints. One has even set up a Change.org petition to beg for a pause on firmware updates until a fix is found.
Facebook

NSO Employees Take Legal Action Against Facebook For Banning Their Accounts (vice.com) 53

On Tuesday, lawyers representing current and former employees of Israeli surveillance contractor NSO Group took legal action against Facebook to try and get their accounts reinstated after being banned by the social media giant. Motherboard reports: Last month, Facebook itself sued NSO in California for leveraging a vulnerability in the WhatsApp chat program that NSO Group clients used to hack targets. As part of that, Facebook also banned the personal Facebook and Instagram accounts of multiple current and former NSO employees. The new lawsuit argues that Facebook violated its own terms of service by blocking the NSO employees, and it used personal information they shared with Facebook in order to identify them, in violation of an Israeli privacy law. As relief, the lawyers ask the court to make Facebook lift the ban on the accounts. The lawsuit was first reported in Israeli media.

"It appears that Facebook used the [NSO employees'] personal data...in order to identify them as NSO employees (or former employees), in service of imposing 'collective punishment' on them, in the form of blocking their personal accounts," the lawsuit reads in Hebrew. The lawsuit argues that the personal data used to identify them as NSO employees belonged to the individuals, and not Facebook. The legal action says that the NSO employees were banned without warning even though they are "private people, who make private use of the social networks, whose only 'sin' was any association with NSO, as employees or former employees." The lawsuit includes a screenshot of an email Facebook allegedly sent to someone who had their account suspended.
Facebook told Motherboard in a statement on Tuesday, "In October we filed a legal complaint which attributed a sophisticated cyber attack to the NSO Group and its employees that was directed at WhatsApp and its users in violation of our terms of service and U.S. law. Such actions warranted disabling relevant accounts and continue to be necessary for security reasons, including preventing additional attacks."
Security

Amazon's Ring Planned Neighborhood 'Watch Lists' Built On Facial Recognition (theintercept.com) 68

An anonymous reader quotes a report from The Intercept: Ring, Amazon's crimefighting surveillance camera division, has crafted plans to use facial recognition software and its ever-expanding network of home security cameras to create AI-enabled neighborhood "watch lists," according to internal documents reviewed by The Intercept. The planning materials envision a seamless system whereby a Ring owner would be automatically alerted when an individual deemed "suspicious" was captured in their camera's frame, something described as a "suspicious activity prompt."

It's unclear who would have access to these neighborhood watch lists, if implemented, or how exactly they would be compiled, but the documents refer repeatedly to law enforcement, and Ring has forged partnerships with police departments throughout the U.S., raising the possibility that the lists could be used to aid local authorities. The documents indicate that the lists would be available in Ring's Neighbors app, through which Ring camera owners discuss potential porch and garage security threats with others nearby. [...] Mohammad Tajsar, an attorney with the American Civil Liberties Union of Southern California, expressed concern over Ring's willingness to plan the use of facial recognition watch lists, fearing that "giving police departments and consumers access to 'watch listing' capabilities on Ring devices encourages the creation of a digital redline in local neighborhoods, where cops in tandem with skeptical homeowners let machines create lists of undesirables unworthy of entrance into well-to-do areas."
When reached for comment, Ring spokesperson Yassi Shahmiri said that "the features described are not in development or in use and Ring does not use facial recognition technology."

Amazon also told Massachusetts Sen. Edward Markey earlier this month that facial recognition has been a "contemplated but unreleased feature" for Ring, but would only be added with "thoughtful design including privacy, security and user control."
Security

Some Fortinet Products Shipped With Hardcoded Encryption Keys (zdnet.com) 21

Fortinet, a vendor of cyber-security products, took between 10 and 18 months to remove a hardcoded encryption key from three products that were exposing customer data to passive interception. From a report: The hardcoded encryption key was found inside the FortiOS for FortiGate firewalls and the FortiClient endpoint protection software (antivirus) for Mac and Windows. These three products used a weak encryption cipher (XOR) and hardcoded cryptographic keys to communicate with various FortiGate cloud services. The hardcoded keys were used to encrypt user traffic for the FortiGuard Web Filter feature, FortiGuard AntiSpam feature, and FortiGuard AntiVirus feature. A threat actor in a position to observe a user or a company's traffic would have been able to take the hardcoded encryption keys and decrypt this weakly encrypted data stream.
Data Storage

Some HPE SSDs Fail After 3 Years and 9 Months, Company Warns (hpe.com) 113

New submitter AllHail writes: HPE SAS solid state drives are affected by a firmware problem which causes these drives to stop working after 32768 power-on hours (3 years and 9 months). If these drives are not flashed with updated firmware before the failure, the drives and the data on them become unrecoverable at that time. If several of these drives are installed and operated together in a RAID, they are going to fail almost simultaneously. Patch or assume the risk of failure, says Hewlett Packard Enterprise.
Social Networks

Facebook and Twitter Users' Data Exposed Due To Third-Party SDK Bug (thurrott.com) 10

Facebook and Twitter announced on Monday that the companies were notified about malicious software development kits (SDKs) that allowed certain apps to collect users' data from the apps without their permission. Paul Thurrott reports: The main culprits here are One Audience and Mobiburn, developers of the malicious SDKs that apparently paid developers to use the SDKs and secretly collect users data. Twitter noted that the issue isn't due to a vulnerability in its software. The breach was caused by "the lack of isolation between SDKs within an application," according to the company. The company also said that the malicious SDKs could allow apps to access personal information like your email, username, and your last tweet without your permission. "We have evidence that this SDK was used to access people's personal data for at least some Twitter account holders using Android, however, we have no evidence that the iOS version of this malicious SDK targeted people who use Twitter for iOS," the company said. The two social networks said that they will notify the affected users about the breach.
United States

US Tech Sector Skews Younger Than the Workforce As a Whole, Study Finds (wsj.com) 118

An anonymous reader quotes a report from The Wall Street Journal: Older information-technology professionals are being passed over by employers, even as IT job openings soar to record highs and employers say recruiting tech talent is a challenge. The IT workforce in the U.S. skews young: Workers aged 22 to 44 account for 61% of the IT sector, but only 49% of the workforce across all occupations, according to 2019 data compiled by IT trade group CompTIA. On the other side, workers aged 45 and older represent 38% of all IT employees at U.S. companies, while the comparable figure for all occupations is 44%, CompTIA said. The largest gap occurs among workers ages 35 to 44. They make up 29% of the IT workforce, but just 21% of the overall national workforce, said Tim Herbert, CompTIA's senior vice president for research and market intelligence. One problem is that some older IT workers who get too comfortable with their skills risk falling behind, says Michael Solomon, an advisory firm for senior technology job seekers. Another issue is cost.

"By the time many tech workers are in their 50s and 60s, they often have top-level compensation packages," the report says. "The age imbalance between IT and the overall U.S. workforce began roughly a decade ago and has grown over the years, researchers have found."
Operating Systems

Zorin OS 15 Lite Linux Distro Can Rejuvenate Your Aging Windows PC (betanews.com) 69

An anonymous reader writes: Called "Zorin OS 15 Lite," it is not only lightweight, but thanks to the Xfce desktop environment and integrated Flatpak support, it should be quite familiar to those switching from Windows. In fact, the developers are intentionally targeting existing Windows 7 users, as Microsoft's operating system will be unsupported beginning January 2020. Zorin OS 15 Lite, in comparison, is based on Ubuntu 18.04 LTS and supported until 2023! It even comes with the very modern Linux kernel 5.0. "With Zorin OS 15 Lite, we've condensed the full Zorin OS experience into a streamlined operating system, designed to run fast on computers as old as 15 years. With version 15, we've gone the extra mile to make the XFCE 4.14-based desktop feel familiar and user-friendly to new users, especially those moving away from Windows 7 leading up to the end of its support in January 2020. By pairing the most advanced and efficient software with a user-friendly experience, we've made it possible for anyone to extend the lifespan of their computers for years to come," explains the Zorin OS developers.

Slashdot Top Deals