Google

Google Chrome To Get Warnings For 'Lookalike URLs' (zdnet.com) 40

Google Chrome browser is set to add a feature that will warn users when accessing sites with domain names that look like authentic websites. From a report: The feature has been in the works for quite some time at Google and is a response to the practice of using typosquatted domains or IDN homograph attacks to lure users on websites they didn't intend to access. Since the release of Chrome Canary 70, Google engineers have been testing a new feature called "Navigation suggestions for lookalike URLs." In Chrome Canary distributions -- Google Chrome's testing ground for new features -- users can access the following URL to enable the feature: chrome://flags/#enable-lookalike-url-navigation-suggestions.
Google

Google+ Reveals Shutdown Timeline For Consumers (androidpolice.com) 31

An anonymous reader quotes a report from Android Police: Google announced its plans to sunset its Google+ social media network for consumers on a sour note in October. The platform, which has a small but dedicated user-base, decided to shut down following Google's acknowledgement of a data exposure that affected up to 500,000 Google+ profiles. Shortly after, in December, the shutdown timeline was expedited due to another, larger bug that had the potential to reveal private user information and impacted approximately 52.5 million users. Now, the company has detailed its shutdown timeline for the consumer version of Google+ -- and it's not wasting any time.

The shutdown timeline is as follows:
- As early as February 4th, you will no longer be able to create new Google+ profiles, pages, communities, or events.
- The Google+ feature for website comments will be removed by Blogger by February 4th and other sites by March 7th. All Google+ comments on all sites will be deleted starting April 2nd.
- Google+ sign-in buttons will stop working in the coming weeks, but in some cases will be replaced by a Google sign-in button.
- Google+ Community owners and moderators who are downloading data from their Community will gain additional data for download starting early March 2019. That includes author, body, and photos for every community post in a public community.
-On April 2nd, all Google+ accounts and pages will be shut down and Google will begin deleting content from consumer Google+ accounts. Photos and videos from Google+ in users' Album Archive and Google+ pages will also be deleted. Photos and videos backed up in Google Photos will not be deleted.

Privacy

Ask Slashdot: What Could Go Wrong In Tech That Hasn't Already Gone Wrong? 367

dryriver writes: If you look at the last 15 years in tech, just about everything that could go wrong seemingly has gone wrong. Everything you buy and bring into your home tracks you in some way or the other. Some software can only be rented now -- no permanent licenses available to buy. PC games are tethered into cloud crap like Steam, Origin and UPlay. China is messing with unborn baby genes. Drones have managed to mess up entire airports. The Scandinavians have developed a serious hatred of cash money and are instead getting themselves chipped. CPUs have horrible security. Every day some huge customer database somewhere gets pwned by hackers. Cybercrime has gone through the roof. You cannot trust the BIOS on your PC anymore. Windows 10 just will not stop updating itself. And AI is soon going to kill us all, if a self-driving car by Uber doesn't do it first. So: What has -- so far -- not gone wrong in tech that still could go wrong, and perhaps in a surprising way?
Facebook

Facebook Pays Teens To Install VPN That Spies On Them (techcrunch.com) 82

A new report from TechCrunch details how "desperate" Facebook is for data on its competitors. The social media company "has been secretly paying people to install a 'Facebook Research' VPN that lets the company suck in all of a user's phone and web activity," a TechCrunch investigation confirms. "Facebook sidesteps the App Store and rewards teenagers and adults to download the Research app and give it root access in what may be a violation of Apple policy so the social network can decrypt and analyze their phone activity." From the report: Since 2016, Facebook has been paying users ages 13 to 35 up to $20 per month plus referral fees to sell their privacy by installing the iOS or Android "Facebook Research" app. Facebook even asked users to screenshot their Amazon order history page. The program is administered through beta testing services Applause, BetaBound and uTest to cloak Facebook's involvement, and is referred to in some documentation as "Project Atlas" a fitting name for Facebook's effort to map new trends and rivals around the globe.

We asked Guardian Mobile Firewall's security expert Will Strafach to dig into the Facebook Research app, and he told us that "If Facebook makes full use of the level of access they are given by asking users to install the Certificate, they will have the ability to continuously collect the following types of data: private messages in social media apps, chats from in instant messaging apps -- including photos/videos sent to others, emails, web searches, web browsing activity, and even ongoing location information by tapping into the feeds of any location tracking apps you may have installed." It's unclear exactly what data Facebook is concerned with, but it gets nearly limitless access to a user's device once they install the app.

Bug

Apple Was Notified About Major FaceTime Eavesdropping Bug Over a Week Ago (macrumors.com) 54

An anonymous reader writes: Twitter user MGT7500 tagged the official Apple Support account in a January 20 tweet claiming that her 14-year-old son discovered a "major security flaw" that allowed him to "listen in to your iPhone/iPad without your approval." The user also tagged Tim Cook on the issue in a follow-up tweet on January 21."

Once the bug started making headlines on Monday, the Twitter user then shared additional tweets claiming that they had also emailed Apple's product security team over a week ago. A screenshot of the email was shared, and it appears the team did respond, but what they said is not visible in the screenshot. [...] All in all, there is evidence that Apple Support was tagged about an eavesdropping bug eight days before it made headlines, and if the rest of the tweets are truthful, the company was also alerted about the bug via several other avenues.
The original story has been updated to include another example of a user -- John Meyer -- who has shared a video about the FaceTime bug that he says was recorded and sent to Apple on January 23.
United States

US Judge Rejects Yahoo Data Breach Settlement (reuters.com) 21

A U.S. judge rejected Yahoo's proposed settlement with millions of people whose email addresses and other personal information were stolen in the largest data breach in history, faulting the Internet services provider for a lack of transparency. From a report: In a Monday night decision, U.S. District Judge Lucy Koh in San Jose, California, said she could not declare the settlement "fundamentally fair, adequate and reasonable" because it did not say how much victims could expect to recover. Yahoo, now part of New York-based Verizon Communications, was accused of being too slow to disclose three breaches from 2013 to 2016 that affected an estimated 3 billion accounts. The settlement called for a $50 million payout, plus two years of free credit monitoring for about 200 million people in the United States and Israel with nearly 1 billion accounts.
Security

Singapore HIV Registry Data Leaked Online in Health Breach (bbc.com) 61

Confidential data about more than 14,000 people diagnosed with HIV, including foreign visitors, has been stolen in Singapore and leaked online. From a report: Authorities revealed details about the 2016 health data breach on Monday. They believe an HIV-positive American whose partner was a senior Singaporean doctor is behind the leak. The hack comes just months after the records of 1.5m Singaporeans, including Prime Minister Lee Hsien Loong, were stolen last year. Confidential information including names, addresses, HIV status and other medical information is reportedly included in the latest breach. Officials say the details of 5,400 Singaporeans and 8,800 foreigners dating up to January 2013 have been compromised.
Communications

All-Photonic Quantum Repeaters Could Lead To a Faster, More Secure Global Quantum Internet (phys.org) 54

"University of Toronto Engineering professor Hoi-Kwong Lo and his collaborators have developed a prototype for a key element for all-photonic quantum repeaters, a critical step in long-distance quantum communication," reports Phys.Org. This proof-of-principle device could serve as the backbone of a future quantum internet. From the report: In light of [the security issues with today's internet], researchers have proposed other ways of transmitting data that would leverage key features of quantum physics to provide virtually unbreakable encryption. One of the most promising technologies involves a technique known as quantum key distribution (QKD). QKD exploits the fact that the simple act of sensing or measuring the state of a quantum system disturbs that system. Because of this, any third-party eavesdropping would leave behind a clearly detectable trace, and the communication can be aborted before any sensitive information is lost. Until now, this type of quantum security has been demonstrated in small-scale systems. Lo and his team are among a group of researchers around the world who are laying the groundwork for a future quantum Internet by working to address some of the challenges in transmitting quantum information over great distances, using optical fiber communication.

Because light signals lose potency as they travel long distances through fiber-optic cables, devices called repeaters are inserted at regular intervals along the line. These repeaters boost and amplify the signals to help transmit the information along the line. But quantum information is different, and existing repeaters for quantum information are highly problematic. They require storage of the quantum state at the repeater sites, making the repeaters much more error prone, difficult to build, and very expensive because they often operate at cryogenic temperatures. Lo and his team have proposed a different approach. They are working on the development of the next generation of repeaters, called all-photonic quantum repeaters, that would eliminate or reduce many of the shortcomings of standard quantum repeaters.
"We have developed all-photonic repeaters that allow time-reversed adaptive Bell measurement," says Lo. "Because these repeaters are all-optical, they offer advantages that traditional -- quantum-memory-based matter -- repeaters do not. For example, this method could work at room temperature."
Privacy

A Bug in FaceTime Allows One To Access Someone's iPhone Camera And Microphone Before They Answered the Call; Apple Temporarily Disables Group FaceTime Feature (thenextweb.com) 88

Social media sites lit up today with anxious Apple users after a strange glitch in iPhone's FaceTime app became apparent. The issue: It turns out that an iPhone user can call another iPhone user and listen in on -- and access live video feed of -- that person's conversations through the device's microphone and camera -- even if the recipient does not answer the call. In a statement, Apple said it was aware of the bug and was working to release a fix later this week. In the meanwhile, the company has disabled Group calling functionality on FaceTime app. From a report: The issue was so serious that Twitter CEO Jack Dorsey, and even Andrew Cuomo, governor of the state of New York, weighed in and urged their followers to disable FaceTime. [...] That's bad news for a company that's been vocal about privacy and customer data protection lately. The timing couldn't be worse, given that Apple is set to host its earnings call for the October-December quarter of 2018 in just a matter of hours.
Wireless Networking

Location Finds Bluetooth, Ultra-Wideband (eetimes.com) 32

An update of the Bluetooth specification released today enables location services accurate to within 10 centimeters thanks to a new direction-finding capability. From a report: It arrives as a separate draft standard is nearly ready for an even faster and more accurate capability using ultra-wideband (UWB) radio, geared for use in smartphones. Bluetooth 5.1 describes ways to determine location using multiple antennas at either the transmitter or receiver. It uses measures of signal phase and amplitude to measure location, though profiles for application developers are still being finished.

In mid-March, the IEEE 802.15.4z standard for UWB should be in a stable draft form, opening the door for silicon designs. It enables location measures within a single centimeter and resolves in a nanosecond, a rate faster than Bluetooth. Smartphone giants Apple and Samsung have been active in the .4z meetings also attended by Huawei, leading some to suggest that the capability could be integrated in handsets within two years. NXP has also been active since the group started a year ago, giving rise to speculation that UWB could come into phones though an integrated NFC chip.

Japan

Japanese Government Plans To Hack Into Citizens' IoT Devices (zdnet.com) 96

An anonymous reader writes: The Japanese government approved a law amendment on Friday that will allow government workers to hack into people's Internet of Things devices as part of an unprecedented survey of insecure IoT devices. The survey will be carried out by employees of the National Institute of Information and Communications Technology (NICT) under the supervision of the Ministry of Internal Affairs and Communications.

NICT employees will be allowed to use default passwords and password dictionaries to attempt to log into Japanese consumers' IoT devices. The plan is to compile a list of insecure devices that use default and easy-to-guess passwords and pass it on to authorities and the relevant internet service providers, so they can take measures to alert consumers and secure the devices. The survey is scheduled to kick off next month, when authorities plan to test the password security of over 200 million IoT devices, beginning with routers and web cameras. Devices in people's homes and on enterprise networks will be tested alike

Bug

Do Debian APT and PHP Pear Patches Highlight Vulnerability In Package Management Infrastructure? (eweek.com) 48

"Time and again, security experts and vendors alike will recommend to organizations and end users to keep software and systems updated with the latest patches," reports eWeek. "But what happens when the application infrastructure that is supposed to deliver those patches itself is at risk?" That's what open-source and Linux users were faced with this past week with a pair of projects reporting vulnerabilities. On January 22, the Debian Linux distribution reported a vulnerability in its APT package manager that is used by end users and organizations to get application updates. That disclosure was followed a day later, on January 23, with the PHP PEAR (PHP Extension and Application Repository) shutting down its primary website, warning that it was the victim of a data breach. PHP PEAR is a package manager that is included with many Linux distributions as part of the open-source PHP programming language binaries....

In the Debian APT case, a security researcher found a flaw, reported it, and the open-source project community responded rapidly, fixing the issue. With PHP PEAR issue, researchers with the Paranoids FIRE (Forensics, Incident Response and Engineering) Team reported that they discovered a tainted file on the primary PEAR website... Both PHP PEAR and Debian have issued updates fixing their respective issues. While both projects are undoubtably redoubling their efforts now with different security technologies and techniques, the simple fact is that the two issues highlight a risk with users trusting updating tools and package management systems.

Privacy

Millions of Bank Loan and Mortgage Documents Have Leaked Online (techcrunch.com) 43

An anonymous reader quotes a report from TechCrunch: [M]illions of documents were found leaking after an exposed Elasticsearch server was found without a password. The documents contained highly sensitive financial data on tens of thousands of individuals who took out loans or mortgages over the past decade with U.S. financial institutions. The documents were converted using a technology called OCR from their original paper documents to a computer readable format and stored in the database, but they weren't easy to read. That said, it was possible to discern names, addresses, birth dates, Social Security numbers and other private financial data by anyone who knew where to find the server. Independent security researcher Bob Diachenko and TechCrunch traced the source of the leaking database to a Texas-based data and analytics company, Ascension. When reached, the company said that one of its vendors, OpticsML, a New York-based document management startup, had mishandled the data and was to blame for the data leak.

It turns out that data was exposed again -- but this time, it was the original documents. Diachenko found the second trove of data in a separate exposed Amazon S3 storage server, which too was not protected with a password. Anyone who went to an easy-to-guess web address in their web browser could have accessed the storage server to see -- and download -- the files stored inside. The bucket contained 21 files containing 23,000 pages of PDF documents stitched together -- or about 1.3 gigabytes in size. Diachenko said that portions of the data in the exposed Elasticsearch database on Wednesday matched data found in the Amazon S3 bucket, confirming that some or all of the data is the same as what was previously discovered. Like in Wednesday's report, the server contained documents from banks and financial institutions across the U.S., including loans and mortgage agreements. We also found documents from the U.S. Department of Housing and Urban Development, as well as W-2 tax forms, loan repayment schedules and other sensitive financial information. Many of the files also contained names, addresses, phone numbers, Social Security numbers and more.

China

The Messy Truth About Infiltrating Computer Supply Chains (theintercept.com) 69

In October last year, Bloomberg Businessweek published an alarming story: Operatives working for China's People's Liberation Army had secretly implanted microchips into motherboards made in China and sold by U.S.-based Supermicro. While Bloomberg's story -- which has been challenged by numerous players -- may well be completely (or partly) wrong, the danger of China compromising hardware supply chains is very real, judging from classified intelligence documents, reports The Intercept. From the report: U.S. spy agencies were warned about the threat in stark terms nearly a decade ago and even assessed that China was adept at corrupting the software bundled closest to a computer's hardware at the factory, threatening some of the U.S. government's most sensitive machines, according to documents provided by National Security Agency whistleblower Edward Snowden. The documents also detail how the U.S. and its allies have themselves systematically targeted and subverted tech supply chains, with the NSA conducting its own such operations, including in China, in partnership with the CIA and other intelligence agencies. The documents also disclose supply chain operations by German and French intelligence.

What's clear is that supply chain attacks are a well-established, if underappreciated, method of surveillance -- and much work remains to be done to secure computing devices from this type of compromise. "An increasing number of actors are seeking the capability to target ... supply chains and other components of the U.S. information infrastructure," the intelligence community stated in a secret 2009 report. "Intelligence reporting provides only limited information on efforts to compromise supply chains, in large part because we do not have the access or technology in place necessary for reliable detection of such operations."

Communications

Zuckerberg Plans To Integrate WhatsApp, Instagram and Facebook Messenger (nytimes.com) 126

Mark Zuckerberg, Facebook's chief executive, plans to integrate the social network's messaging services -- WhatsApp, Instagram and Facebook Messenger -- asserting his control over the company's sprawling divisions at a time when its business has been battered by scandals.

The New York Times: The move, described by four people involved in the effort, requires thousands of Facebook employees to reconfigure how WhatsApp, Instagram and Facebook Messenger function at their most basic levels. While all three services will continue operating as stand-alone apps, their underlying messaging infrastructure will be unified, the people said. Facebook is still in the early stages of the work and plans to complete it by the end of this year or in early 2020, they said.

Mr. Zuckerberg has also ordered all of the apps to incorporate end-to-end encryption, the people said, a significant step that protects messages from being viewed by anyone except the participants in the conversation. After the changes take effect, a Facebook user could send an encrypted message to someone who has only a WhatsApp account, for example. Currently, that isn't possible because the apps are separate.

Chrome

Chrome API Update Will Kill a Bunch of Other Extensions, Not Just Ad Blockers (zdnet.com) 93

An anonymous reader writes: A planned update to one of the Google Chrome extensions APIs would kill much more than a few ad blockers, ZDNet has learned, including browser extensions for antivirus products, parental control enforcement, phishing detection, and various privacy-enhancing services. Developers for extensions published by F-Secure, NoScript, Amnesty International, and Ermes Cyber Security, among others, made their concerns public today after news broke this week that Google was considering the API change. Furthermore, efforts to port NoScript from Firefox to Chrome are also impacted, according to the plugin's author, who says the new API update all but cripples the NoScript for Chrome port.
Security

How Web Apps Can Turn Browser Extensions Into Backdoors (threatpost.com) 34

"Threatpost has a link to some recent research about ways web pages can exploit browser extensions to steal information or write files," writes Slashdot reader jbmartin6. "Did we need another reason to be deeply suspicious of any browser extension? Not only do they spy on us for their makers, now other people can use them to spy on us as well. The academic paper is titled 'Empowering Web Applications with Browser Extensions' (PDF)." From the report: "An attacker [uses] a script that is present in a web application currently running in the user browser. The script either belongs to the web application or to a third party. The goal of the attacker is to interact with installed extensions, in order to access user sensitive information. It relies on extensions whose privileged capabilities can be exploited via an exchange of messages with scripts in the web application," researchers wrote. They added, "Even though content scripts, background pages and web applications run in separate execution contexts, they can establish communication channels to exchange messages with one another... APIs [are used] for sending and receiving (listening for) messages between the content scripts, background pages and web applications."

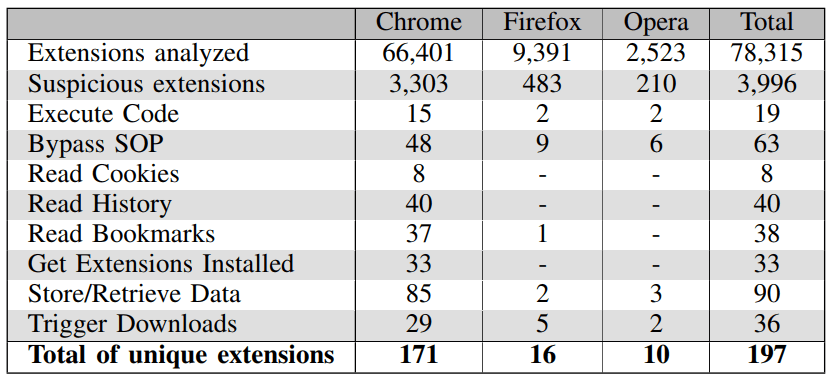
The researcher behind the paper focused on a specific class of web extension called "WebExtensions API," a cross-browser extensions system compatible with major browsers including Chrome, Firefox, Opera and Microsoft Edge. After analyzing 78,315 extensions that used the specific WebExtension API, it found 3,996 that were suspicious. While it seems voluminous, they noted that research found a small number of vulnerable extensions overall, and that concern should be measured. However, "browser vendors need to review extensions more rigorously, in particular take into consideration the use of message passing interfaces in extensions."

Security

France Will Hack Its Enemies Back, Its Defense Secretary Says (theregister.co.uk) 71

France's defence secretary Florence Parly had a declaration to make this week: "Cyber war has begun." And she said the Euro nation's military will use its "cyber arms as all other traditional weapons... to respond and attack," as well as setting up a military bug bounty program. From a report: Parly made her pledges during a speech to the Forum International de Cybersecurite (FIC) in the northern French town of Lille. Her speech was on a topic that most Western countries shy away from addressing directly in public. "The cyber weapon is not only for our enemies," said France's defence secretary this afternoon, speaking through a translator. "No. It's also, in France, a tool to defend ourselves. To respond and attack." Her remarks will be seen as moving the debate about offensive cyber capabilities -- not just so-called "active defence" but using infosec techniques as another weapon in the arsenal of state-on-state warfare -- to a new level.
Bitcoin

New Ransomware Strain is Locking Up Bitcoin Mining Rigs in China (zdnet.com) 86

A new strain of ransomware has been observed targeting Bitcoin mining rigs. ZDNet reports: At the time of writing, most of the infections have been reported in China, the country where most of the world's cryptocurrency mining farms are located. Named hAnt, this new ransomware strain was first seen in August of last year, but a new wave of infections has been reported hitting mining farms earlier this month. Most of the infected mining rigs are Antminer S9 and T9 devices, used for Bitcoin mining, but there have also been reports of hAnt infecting Antminer L3 rigs, used for mining Litecoin. In rare instances, Avalon Miner equipment (used for Bitcoin), were also reported as infected, but in much smaller numbers.
Security

More Than Half of PC Applications Installed Worldwide Are Out-of-Date (helpnetsecurity.com) 151

Avast's PC Trends Report 2019 found [PDF] that users are making themselves vulnerable by not implementing security patches and keeping outdated versions of popular applications on their PCs. From a news report: The applications where updates are most frequently neglected include Adobe Shockwave (96%), VLC Media Player (94%) and Skype (94%). The report, which uses anonymized and aggregated data from 163 million devices across the globe, also found that Windows 10 is now installed on 40% of all PCs globally, which is fast approaching the 43% share held by Windows 7. However, 15% of all Windows 7 users and 9% of all Windows 10 users worldwide are running older and no longer supported versions of their product, for example, the Windows 7 Release to Manufacturing version from 2009 or the Windows 10 Spring Creators Update from early 2017.

Slashdot Top Deals