Security

You Can Now Check If Your ISP Uses Basic Security Measures (wired.com) 28

"Is BGP Safe Yet" is a new site that names and shames internet service providers that don't tend to their routing. From a report: For more than an hour at the beginning of April, major sites like Google and Facebook sputtered for large swaths of people. The culprit wasn't a hack or a bug. It was problems with the internet data routing standard known as the Border Gateway Protocol, which had allowed significant amounts of web traffic to take an unexpected detour through a Russian telecom. For Cloudflare CEO Matthew Prince, it was the last straw. BGP disruptions happen frequently, generally by accident. But BGP can also be hijacked for large-scale spying, data interception, or as a sort of denial of service attack.

[...] On Friday, the company launched Is BGP Safe Yetâ, a site that makes it easier for anyone to check whether their internet service provider has added the security protections and filters that can make BGP more stable. Those improvements are most effective with wide adoption from ISPs, content delivery networks like Cloudflare, and other cloud providers. Cloudflare estimates that so far about half of the internet is more protected thanks to heavy hitters like AT&T, the Swedish telecom Telia, and the Japanese telecom NTT adopting BGP improvements. And while Cloudflare says it doesn't seem like the Rostelecom incident was intentional or malicious, Russian telecoms do have a history of suspicious BGP meddling, and similar problems will keep cropping up until the whole industry is on board.

Security

Cognizant Confirms Maze Ransomware Attack, Says Customers Face Disruption (techcrunch.com) 9

Cognizant, one of the largest tech and consulting companies in the Fortune 500, has confirmed it was hit by a ransomware attack. From a report: Details remain slim besides a brief statement on its site, confirming the incident. "Cognizant can confirm that a security incident involving our internal systems, and causing service disruptions for some of our clients, is the result of a Maze ransomware attack," the statement read. "Our internal security teams, supplemented by leading cyber defense firms, are actively taking steps to contain this incident." The New Jersey-headquartered IT giant said it was engaging with the law enforcement.

The company, which offers a range of services including IT consultation to clients in more than 80 countries, posted $16.8 billion in revenue last year. The decades-old firm also maintains a business agreement with Facebook to help the social giant moderate content on its platform. Cognizant employs about 290,000 people, most of whom live in India. Maze is not like typical data-encrypting ransomware. Maze not only spreads across a network, infecting and encrypting every computer in its path, it also exfiltrates the data to the attackers' servers where it is held for ransom.

Security

Zoom's Security Woes Were No Secret to Business Partners Like Dropbox (nytimes.com) 33

Dropbox privately paid top hackers to find bugs in software by the videoconferencing company Zoom, then pressed it to fix them. From a report: One year ago, two Australian hackers found themselves on an eight-hour flight to Singapore to attend a live hacking competition sponsored by Dropbox. At 30,000 feet, with nothing but a slow internet connection, they decided to get a head start by hacking Zoom, a videoconferencing service that they knew was used by many Dropbox employees. The hackers soon uncovered a major security vulnerability in Zoom's software that could have allowed attackers to covertly control certain users' Mac computers. It was precisely the type of bug that security engineers at Dropbox had come to dread from Zoom, according to three former Dropbox engineers.

Now Zoom's videoconferencing service has become the preferred communications platform for hundreds of millions of people sheltering at home, and reports of its privacy and security troubles have proliferated. Zoom's defenders, including big-name Silicon Valley venture capitalists, say the onslaught of criticism is unfair. They argue that Zoom, originally designed for businesses, could not have anticipated a pandemic that would send legions of consumers flocking to its service in the span of a few weeks and using it for purposes -- like elementary school classes and family celebrations -- for which it was never intended.

[...] The former Dropbox engineers, however, say Zoom's current woes can be traced back two years or more, and they argue that the company's failure to overhaul its security practices back then put its business clients at risk. Dropbox grew so concerned that vulnerabilities in the videoconferencing system might compromise its own corporate security that the file-hosting giant took on the unusual step of policing Zoom's security practices itself, according to the former engineers, who spoke on the condition of anonymity because they were not authorized to publicly discuss their work. As part of a novel security assessment program for its vendors and partners, Dropbox in 2018 began privately offering rewards to top hackers to find holes in Zoom's software code and that of a few other companies. The former Dropbox engineers said they were stunned by the volume and severity of the security flaws that hackers discovered in Zoom's code -- and troubled by Zoom's slowness in fixing them.

Security

After 8 Years of Remote-Access Trojans Attacks, Can We Still Say Linux is Secure? (linuxsecurity.com) 139

Remember when BlackBerry reported Advanced Persistent Threat groups have been infiltrating critical Linux servers for at least eight years? What's the lesson to be learned?

LinuxSecurity Founder Dave Wreski argues "Although it may be easy to blame the rise in attacks targeting Linux in recent years on security vulnerabilities in the operating system as a whole, this is simply not the truth. The majority of exploits on Linux systems can be attributed to misconfigured servers and poor administration."

Writing for Linux Security, Slashdot reader b-dayyy gathered some additional responses: Some experts argue that it is the popularity of Linux that makes it a target. Joe McManus, Director of Security at Canonical, explains: "Linux and, particularly Ubuntu, are incredibly secure systems but, that being said, it is their popularity that makes them a target." Ian Thornton-Trump, a threat intelligence expert and the CISO at Cyjax, adds: "From an economic and mission perspective, it makes sense for a threat actor to invest in open-source skills for flexibility and the ability to target the systems where the good stuff is happening."

Despite the increasing number of threats targeting Linux systems, there is still a sound argument for the inherent security of Linux, which can be attributed to the core fundamentals of Open Source. Due to the transparency of open-source code and the constant scrutiny that this code undergoes by a vibrant global community, vulnerabilities are identified and remedied quicker than flaws that exist in the opaque source code of proprietary software and operating systems. Threat actors recognize this, and are still directing the majority of their attacks at proprietary operating systems.

These attacks do; however, serve as a much-needed wakeup call for the security community that more needs to be done to protect Linux servers. BlackBerry's report reveals that security solutions and defensive coverage available within Linux environments is "immature at best". Endpoint protection, detection and response products are inadequately utilized by too many Linux users, and endpoint solutions available for Linux systems are often insufficient in combating advanced exploits. Eric Cornelius, Chief Product Officer at BlackBerry, evaluates: "Security products and services that support Linux, offerings that might detect and give us insight into a threat like this, are relatively lacking compared to other operating systems, and security research about APT use of Linux malware is also relatively sparse."

Netscape

Silicon Valley Legends Launch 'Beyond Identity' To Eliminate All Passwords (securityweek.com) 143

SecurityWeek editor wiredmikey shares new that Jim Clark and Tom Jermoluk (past founders of Netscape, Silicon Graphics and @Home Network) "have launched a phone-resident personal certificate-based authentication and authorization solution that eliminates all passwords."

Security Week reports: The technology used is not new, being based on X.509 certificates and SSL (invented by Netscape some 25 years ago and still the bedrock of secure internet communications). It is the opportunity provided by the modern smartphone with biometric user access, enough memory and power, and a secure enclave to store the private keys of a self-certificate that never leaves the device that is new. The biometric access ties the phone to its user, and the Beyond Identity certificate authenticates the device/user to the service provider, whether that's a bank or a corporate network...

"When this technology was created at Netscape during the beginning of the World Wide Web, it was conceived as a mechanism for websites to securely communicate, but the tools didn't yet exist to extend the chain all the way to the end user," commented Jermoluk. "Beyond Identity includes the user in the same chain of certificates bound together with the secure encrypted transport (TLS) used by millions of websites in secure communications today...."

With no passwords, the primary cause of data breaches (either to steal passwords or by using stolen passwords) is gone. It removes all friction from the access process, takes the password reset load off the help desk, and can form the basis of a zero-trust model where identity is the perimeter.

Though they're first focusing on the corporate market, their solution should be available to consumers by the end of 2020, the article reports, which speculates that the possibility of pre-also installing the solution on devices "is not out of the question."
Piracy

The Pirate Bay Blocked By MalwareBytes But Normal Service Will Be Resumed (torrentfreak.com) 16

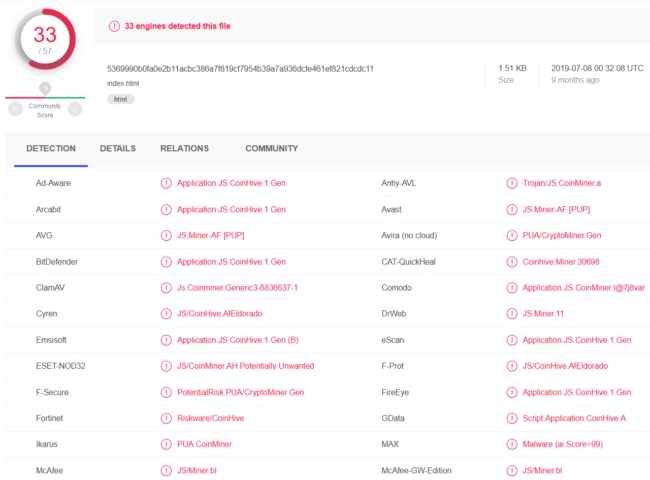
The Pirate Bay returned to the clear web this week after a month-long hiatus. However, the structure of the infamous torrent index presented an access problem to users of the popular anti-malware software MalwareBytes, which persistently blocked an essential element of the platform due to the presence of "a few" cryptocurrency miners on a secondary domain. TorrentFreak reports: The problem lay in The Pirate Bay's setup. Aside from cosmetic changes to some pages, the site sends requests to another domain (apibay.org) in order to present torrents to the user on thepiratebay.org. However, those accessing the main domain with Malwarebytes installed were greeted with blank torrent pages after the security software blocked apibay.org. Any warning of this type, especially concerning trojans, should be of concern to users of any site. However, dumping trojans on users hasn't been the modus operandi of The Pirate Bay thus far, so TorrentFreak contacted Malwarebytes to find out what was causing the alert.

Manager of WebProtection Labs at MalwareBytes Andres Ortiz informs TorrentFreak that the issue was caused by the presence of "a few" cryptocurrency miners, not on thepiratebay.org, but on a sub-directory of apibay.org, the domain from where TPB appears to present its torrent results. The analysis for just one example miner is shown [here]. After examining the apibay.org domain once again, MalwareBytes has now confirmed that the miners have been removed so in response, they will push an update to their users to stop TPB's indexes from being blocked moving forward. However, if any party reintroduces the miners, it's certainly possible that the site will be rendered inaccessible once again.

Security

DHS CISA: Companies Are Getting Hacked Even After Patching Pulse Secure VPNs (zdnet.com) 9

According to the DHS's Cybersecurity and Infrastructure Security Agency (CISA), companies that run Pulse Secure VPN servers are still at risk of getting hacked, despite patching vulnerable systems. ZDNet reports: Pulse Secure VPN servers are enterprise-grade VPN gateways that companies use to let workers connect to internal company networks from across the internet. Last year, a major vulnerability was disclosed in these products. The vulnerability, tracked as CVE-2019-11510, allowed hackers to run malicious code on vulnerable servers. [...] According to the [DHS CISA and Japan's Computer Emergency Response Team (JPCERT)], hackers have also been using access to the Pulse Secure VPN server to extract plaintext Active Directory (AD) credentials.

Now, JPCERT and CISA say they're seeing attacks where hackers are leveraging these stolen credentials to access internal networks even after companies patched Pulse Secure VPN gateways. In an alert published yesterday, CISA said it was aware of "incidents where compromised Active Directory credentials were used months after the victim organization patched their VPN appliance." The U.S. agency has released a tool on GitHub for companies that run Pulse Secure VPNs. The tool can be used to sift through their Pulse Secure logs and spot signs of a potential compromise. The tool scans for IP addresses and user-agents known to be associated with groups that have exploited Pulse Secure VPN servers.

Ruby

Clipboard Hijacking Malware Found in 725 Ruby Libraries (zdnet.com) 22

Security researchers from ReversingLabs say they've discovered 725 Ruby libraries uploaded on the official RubyGems repository that contained malware meant to hijack users' clipboards. From a report: The malicious packages were uploaded on RubyGems between February 16 and 25 by two accounts -- JimCarrey and PeterGibbons. The 725 libraries, which are listed here in full, have been removed two days later, on February 27, after the ReversingLabs team notified the RubyGems security team. All the Ruby libraries were copies of legitimate libraries, used lookalike names, worked as intended, but also contained additional malicious files. The extra file inserted into each package was named aaa.png. However, ReversingLabs say this file wasn't a PNG image, but instead was a Windows PE executable.
Android

The Secret Behind 'Unkillable' Android Backdoor Called xHelper Has Been Revealed (arstechnica.com) 40

An anonymous reader quotes a report from Ars Technica: In February, a researcher detailed a widely circulating Android backdoor that's so pernicious that it survives factory resets, a trait that makes the malware impossible to remove without taking unusual measures. The analysis found that the unusual persistence was the result of rogue folders containing a trojan installer, neither of which was removed by a reset. The trojan dropper would then reinstall the backdoor in the event of a reset. Despite those insights, the researcher still didn't know precisely how that happened. Now, a different researcher has filled in the missing pieces.

Last week, Kaspersky Lab researcher Igor Golovin published a post that filled in some of the gaps. The reinfections, he said, were the result of files that were downloaded and installed by a notorious trojan known as Triada, which ran once the xHelper app was installed. Triada roots the devices and then uses its powerful system rights to install a series of malicious files directly into the system partition. It does this by remounting the system partition in write mode. To make the files even more persistent, Triada gives them an immutable attribute, which prevents deleting, even by superusers. (Interestingly, the attribute can be deleted using the chattr command.) A file named install-recovery.sh makes calls to files added to the /system/xbin folder. That allows the malware to run each time the device is rebooted. The result is what Golovin described as an "unkillable" infection that has extraordinary control over a device.

Privacy

India Says Zoom 'Not a Safe Platform' For Video Conferencing (reuters.com) 49

India is the latest country to denounce videoconferencing software Zoom, calling it "not a safe platform." Reuters reports: "Zoom is a not a safe platform," the Cyber Coordination Centre (CyCord) of India's ministry of home affairs said in a 16-page advisory. The government body also provided guidelines on how to avoid unauthorized users from carrying out malicious acts while using the tool. Zoom's mobile app saw a sharp surge in downloads in India as the country enforced a nationwide lockdown late last month to curb the spread of the coronavirus. Even some Indian government officials have held discussions with industry executives to discuss coronavirus relief measures via Zoom. One media report this week said the Indian government was advising its ministers not to use third-party software for sensitive meetings.
IT

Pastebin Made It Harder To Scrape Its Site And Researchers Are Pissed Off (vice.com) 27

The most famous paste site, used by hackers of all stripes to host lists of stolen passwords, announcements of data breaches, and malware has made it harder for security researchers to scrape it looking for that kind of information. From a report: And security researchers are pissed off. Pastebin is one of the most famous websites that allows anyone, even without being registered, to "paste" any kind of text and make it public. Over the years, it became a repository for all kinds of unsavory data, such as the personal details of people who got doxed by hackers, leaked passwords, hacker manifestos, and even malware payloads. Naturally, this meant it was a treasure trove for security researchers investigating data breaches or hunting hackers. On Tuesday, several security researchers complained on Twitter that they were unable to search Pastebin or scrape it using a special API, which they paid to get access to. (The lifetime subscription, which was required to scrape the site, cost $50.)
AI

AI Spots Critical Microsoft Security Bugs 97% of the Time (venturebeat.com) 41

Microsoft claims to have developed a system that correctly distinguishes between security and non-security software bugs 99% of the time, and that accurately identifies the critical, high-priority security bugs on average 97% of the time. From a report: In the coming months, it plans to open-source the methodology on GitHub, along with example models and other resources. Their work suggests that such a system, which was trained on a data set of 13 million work items and bugs from 47,000 developers at Microsoft stored across AzureDevOps and GitHub repositories, could be used to support human experts. It's estimated that developers create 70 bugs per 1,000 lines of code and that fixing a bug takes 30 times longer than writing a line of code, and that in the U.S., $113 billion is spent annually on identifying and fixing product defects. In the course of architecting the model, Microsoft says that security experts approved the training data and that statistical sampling was used to provide those experts a manageable amount of data to review. The data was then encoded into representations called feature vectors and Microsoft researchers designed the system using a two-step process, in which the model first learned to classify security and non-security bugs and then to apply severity labels -- critical, important, low-impact -- to the security bugs.
Security

Linksys Asks Users To Reset Passwords After Hackers Hijacked Home Routers Last Month (zdnet.com) 28

Router vendor Linksys has locked user accounts on its Smart WiFi cloud service and is asking them to reset passwords after hackers have been observed hijacking accounts and changing router settings to redirect users to malware sites. From a report: Linksys' decision only impacts Smart WiFi accounts. Linksys Smart WiFi is a cloud-based account system that lets device owners connect to Linksys routers (and other equipment) over the internet to manage router settings. Smart WiFi is widely deployed across Linksys' router fleet, making it an ideal target for hackers who may want to hijack routers en-masse. According to a Bitdefender report published last month, this is exactly what's been recently happening. The cyber-security firm said it detected an organized campaign to break into D-Link and Linksys routers and change DNS settings.
Privacy

Hackers Are Selling a Critical Zoom Zero-Day Exploit for $500,000 (vice.com) 38

Hackers are selling two critical vulnerabilities for the video conferencing software Zoom that would allow someone to hack users and spy on their calls, Motherboard reported Wednesday. From the report: The two flaws are so-called zero-days, and are currently present in Zoom's Windows and MacOS clients, according to three sources who are knowledgeable about the market for these kinds of hacks. The sources have not seen the actual code for these vulnerabilities, but have been contacted by brokers offering them for sale. Zero-day exploits or just zero-days or 0days are unknown vulnerabilities in software or hardware that hackers can take advantage of to hack targets. Depending on what software they're in, they can be sold for thousands or even millions of dollars.

Last week, Motherboard reported that there was an increased interest in zero-days for Zoom as millions of people, including employees and executives at big companies around the world, moved onto the platform for sensitive or confidential meetings, due to the coronavirus pandemic. "From what I've heard, there are two zero-day exploits in circulation for Zoom. [...] One affects OS X and the other Windows," said Adriel Desautels, the founder of Netragard, a company that used to sell and trade zero-days. "I don't expect that these will have a particularly long shelf-life because when a zero-day gets used it gets discovered."

Security

North Korea Hacking Threatens US and Global Financial System: US Officials (reuters.com) 87

U.S. government officials warned on Wednesday about the threat of North Korean hackers, calling particular attention to banking and other finance. From a report: The reason for the advisory -- which was jointly issued by the U.S. Departments of State, Treasury, and Homeland Security, and the Federal Bureau of Investigation -- was unclear. North Korean hackers have long been accused of targeting financial institutions, and the content of the warning appeared to draw on material already in the public domain. North Korea is alleged to be behind an ambitious, years-long campaign of digital theft, including siphoning tens of millions of dollars in cash from ATMs, carrying out gigantic thefts at major banks, extorting computer users worldwide, and hijacking digital currency exchanges. The global money-grab has been a topic of increasing international concern.
Google

Google Is Lowering Nest Camera Quality 'To Conserve Internet Resources' (techcrunch.com) 59

Google is temporarily lowering the video quality of its Nest security cameras to "conserve internet resources" during the COVID-19 pandemic. "The adjustment is rolling out over the next few days, and Google says anyone who has their quality settings adjusted will get a notification in the Nest app," reports TechCrunch. From the report: While Nest cameras aren't inherently using more bandwidth right now than they otherwise might, each camera already used a good amount of bandwidth day to day. A Nest Cam IQ, for example, uses roughly 400GB of data per month at its highest settings; cutting this down to medium high shaves that down to 300GB. Google confirmed their plans with TechCrunch, with a Google spokesperson adding: "To answer the global call to prioritize internet bandwidth for learning and working, in the next few days we're going to be making a few changes. We believe these changes have the potential to help make it easier for communities to keep up with school, work, and everything in between."

While they're automatically making the change on behalf of the user (a move some owners are complaining is an overstep), Google notes that you're able to bump your cameras back up to their highest settings should you see fit. They're not capping the quality, instead just lowering settings by default -- so if you've got a camera in a setting where every pixel counts, know that you're going to need to adjust accordingly.

The Internet

Over 500,000 Zoom Accounts Sold On Hacker Forums, the Dark Web (bleepingcomputer.com) 23

An anonymous reader quotes a report from Bleeping Computer: Over 500,000 Zoom accounts are being sold on the dark web and hacker forums for less than a penny each, and in some cases, given away for free. These credentials are gathered through credential stuffing attacks where threat actors attempt to login to Zoom using accounts leaked in older data breaches. The successful logins are then compiled into lists that are sold to other hackers. Some of these Zoom accounts are offered for free on hacker forums so that hackers can use them in zoom-bombing pranks and malicious activities. Others are sold for less than a penny each.

Cybersecurity intelligence firm Cyble told BleepingComputer that around April 1st, 2020, they began to see free Zoom accounts being posted on hacker forums to gain an increased reputation in the hacker community. These accounts are shared via text sharing sites where the threat actors are posting lists of email addresses and password combinations. The purchased accounts include a victim's email address, password, personal meeting URL, and their HostKey. Cyble has told BleepingComputer that these accounts include ones for well-known companies such as Chase, Citibank, educational institutions, and more.
You can use Have I Been Pwned and Cyble's AmIBreached to check if your email address has been leaked in a data breach.
Chrome

Google Removes 49 Chrome Extensions Caught Stealing Crypto-Wallet Keys (zdnet.com) 18

Google has removed 49 Chrome extensions from the Web Store that posed as legitimate cryptocurrency wallet apps but contained malicious code that stole crypto-wallet private keys, mnemonic phrases, and other raw secrets. From a report: The 49 extensions were discovered by Harry Denley, Director of Security at the MyCrypto platform, who shared his findings exclusively with ZDNet last week. Denley says the 49 extensions appear to have been put together by the same person/group, believed to be a Russian-based threat actor. "Whilst the extensions all function the same, the branding is different depending on the user they are targeting," Denley said. The MyCrypto security researcher says he has identified malicious extensions posing as known crypto-wallets apps such as Ledger, Trezor, Jaxx, Electrum, MyEtherWallet, MetaMask, Exodus, and KeepKey.
Security

Ransomware Scumbags Leak Boeing, Lockheed Martin, SpaceX Documents After Contractor Refuses To Pay (theregister.co.uk) 152

An anonymous reader quotes a report from The Register: Internal confidential documents belonging to some of the largest aerospace companies in the world have been stolen from an industrial contractor and leaked online. The data was pilfered and dumped on the internet by the criminals behind the DoppelPaymer Windows ransomware, in retaliation for an unpaid extortion demand. The sensitive documents include details of Lockheed-Martin-designed military equipment -- such as the specifications for an antenna in an anti-mortar defense system -- according to a Register source who alerted us to the blueprints. Other documents in the cache include billing and payment forms, supplier information, data analysis reports, and legal paperwork. There are also documents outlining SpaceX's manufacturing partner program.

The files were siphoned from Visser Precision by the DoppelPaymer crew, which infected the contractor's PCs and scrambled its files. When the company failed to pay the ransom by their March deadline, the gang -- which tends to demand hundreds of thousands to millions of dollars to restore encrypted files -- uploaded a selection of the documents to a website that remains online and publicly accessible. Visser is a manufacturing and design contractor in the U.S. whose clients are said to include aerospace, automotive, and industrial manufacturing outfits -- think Lockheed Martin, SpaceX, Tesla, Boeing, Honeywell, Blue Origin, Sikorsky, Joe Gibbs Racing, the University of Colorado, the Cardiff School of Engineering, and others. The leaked files relate to these customers, in particular Tesla, Lockheed Martin, Boeing, and SpaceX.

IT

Thousands of Techies in Locked-Down India Are Braving Coronavirus Daily To Keep the World Running (qz.com) 70

The world's abrupt slowing down in the past few weeks may have introduced millions of Covid-19-wary professionals to the whole new paradigm of work-from-home. Yet, a third of India's four million IT employees are still trudging regularly to the office even if mostly to make life easier for clients abroad. From a report: Every working day, these thousands risk contracting coronavirus, jeopardising even their families' health, by going to work amid India's ongoing 21-day lockdown. Only because their jobs, in cities like Bengaluru, Pune, and Hyderabad, form the backroom spine of some of the world's corporate behemoths. Indian IT majors like Tata Consultancy Services (TCS), Infosys, and Wipro service giants like General Electric, Citibank, Morgan Stanley, Fidelity, HSBC, Lloyds Banking Group, Airbus, Cisco, British Telecom, Vodafone, and Nielsen, among thousands of other companies across the globe.

"We power the financial backbones of several countries, support some of the largest health care and pharmacy companies in the world, run technology for governments and public services organisations," a TCS spokesperson told Quartz when asked about the lockdown. Besides, many global businesses also have essential functions -- accounting, payments, billing, human resources, and payroll -- being carried out in their own back offices in India.

Slashdot Top Deals